Privacy & Data Sovereignty
My Chat Assistant is built to avoid third-party data leaks, invasive tracking cookies, and unauthorized AI model training on user inputs.
Zero Client-Side Tracking
No third-party analytics cookies, advertising beacons, or external tracking scripts are injected into your visitors' browser sessions.
On-Premise Log Isolation
All conversation transcripts and session metadata are stored locally on your host server inside an SQLite database file, not on a third-party platform.
Configurable Retention
Conversation logs default to a 90-day retention window and can be adjusted, purged, or exported to fit your own data handling policy.
Safeguarding Detection
Messages are checked for safeguarding language before any answer is generated. On a match, the product skips content generation entirely and returns a fixed, operator-reviewed response, with a handoff to a person if one is configured. The visitor can keep talking either way.
PII Redaction
Common personal identifiers, an email address, a phone number, a UK National Insurance number, a UK NHS number, and a date of birth, are stripped from what gets stored, on every message. Your site content and an operator's own Q&A entries are untouched.
No Model Training Leakage
Your documentation and proprietary knowledge base queries are never submitted to public LLM dataset pools for external model training.
What Happens to What a Visitor Types
Both safeguarding detection and PII redaction run locally, before anything reaches an AI provider, and both are on by default. Neither is a black box: an operator can see them in the dashboard and turn them off or adjust them if a different configuration is needed. Safeguarding detection works from a defined keyword list, not a clinical or risk assessment of the person typing, and PII redaction covers a defined, small set of common identifier patterns rather than every kind of personal data a message could contain. These are product capabilities that support a compliance program, not a certification in themselves.
For the full picture, including what's built in, what depends on your own configuration, and what we haven't independently verified yet, see Trust & Compliance.
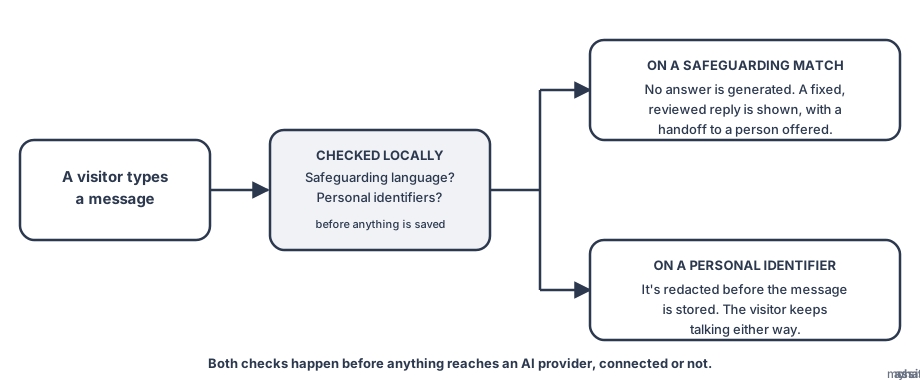
What happens to a message before it's stored — checked locally, before it ever reaches an AI provider.
Data Retention & Control
Because all data resides within your own hosting infrastructure, full data retention and erasure schedules remain completely within your team's control. You can run automated cron jobs to purge, archive, or anonymize session logs at any interval without depending on third-party SaaS vendors.
Request Documentation